Gulf ports are rapidly advancing with AI-powered berth scheduling, interconnected cranes, electric vehicles, and widespread IoT sensors. These smart-port innovations enhance throughput by 20–30%.
However, the rise in automation brings significant cyber risks. Globally, 69% of port cyber incidents involve ransomware, prompting DP World to invest $100 million in 2024 alone to enhance security measures — cutting vulnerabilities by half.
When crises hit, port security leaders confront an unavoidable question: “Did the ship depart on time?”
Smart ports face a daunting task: managing thousands of daily security alerts, with up to 80% being false alarms. This deluge risks overwhelming security teams and missing real threats.
“Ports operate where speed and security are crucial. Intelligent filtering and Deep Observability provide teams with only necessary data, reducing noise. This leads to faster detection, quicker responses, and smooth operations. In port security, packets reveal the true story,” said Damian Wilk, SEMEA General Manager at Gigamon, in an interview with Khaleej Times.
When anomalies arise, the system can take immediate, reversible actions like isolating a suspicious camera network or temporarily disabling a badge reader. “Security analysts focus only on alerts that pass through filtering,” explained Osama Alzoubi, MEA Vice President at Phosphorus.
More alerts don’t equate to better security. Bombarded teams waste time on false warnings, allowing real threats to slip through. “The solution is identifying relevant alerts. Effective analysis merges threat intelligence with patterns of suspicious behavior, filtering out noise. Direct network activity monitoring accelerates problem detection,” stated Dr. Emad Fahmy, Middle East Director of Systems Engineering at Netscout.
In global trade hubs, even brief delays can trigger chain reactions. Logs provide a slow, often incomplete overview, forcing security teams to piece together events from scattered clues.
Packet-level monitoring delivers a comprehensive, tamper-proof record of network activity. This detects suspicious behavior in real-time, minimizing damage window. “A complete, reliable picture speeds up and refines investigations. Security teams act confidently, minimizing disruptions,” Fahmy noted. For ports, this means resolving issues swiftly and maintaining goods movement, Wilk added.
“Feeding this data into automated detection systems helps quickly dismiss false alarms and highlight genuine threats for human review. This speed helps contain issues within minutes, keeping port operations seamless,” Alzoubi mentioned.
Modern ports blend old and new equipment. Decades-old cranes work alongside 5G devices and smart sensors. Each new connection opens potential attack points. Older machines often lack security features, and continuous operations leave little room for updates without disrupting work.
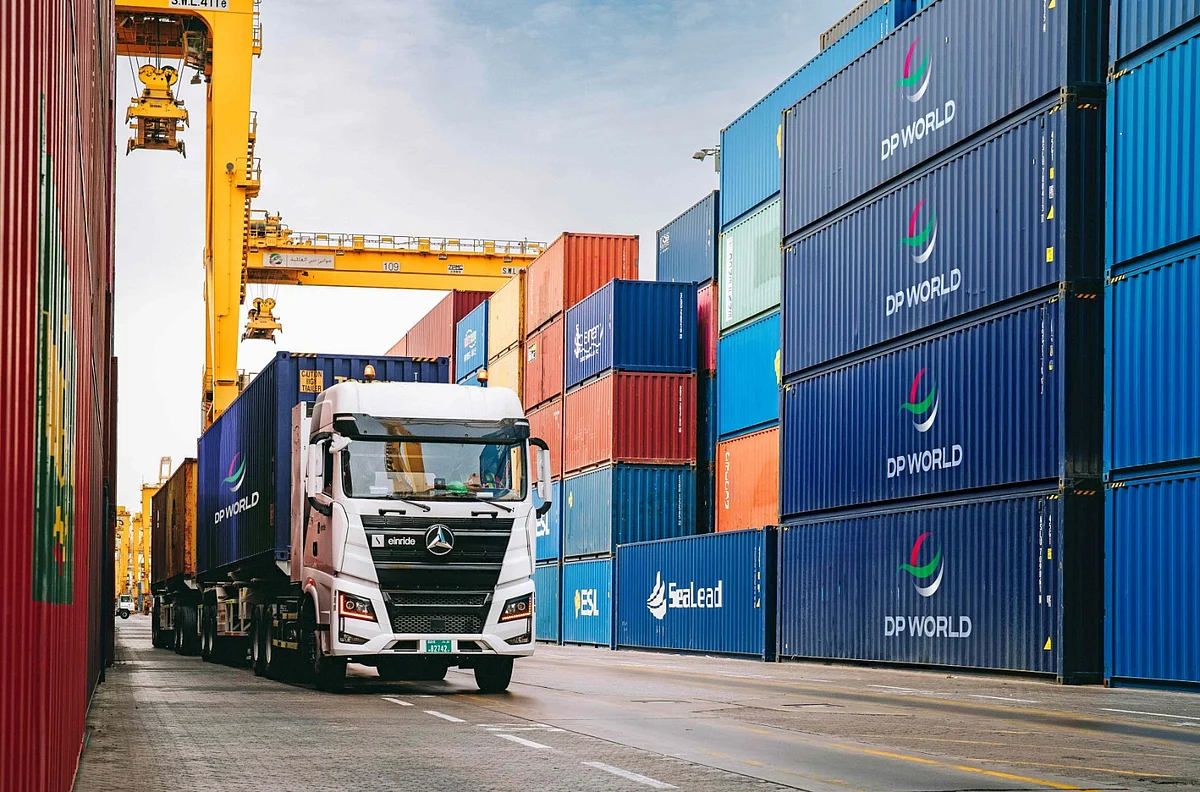
DP World invested $100 million in 2024 alone to upgrade security protocols — resulting in a 50% reduction in vulnerabilities.
“Clear visibility across IT and operational systems enables early problem detection. This includes underperforming or targetable equipment. Real-time network activity monitoring allows for quick issue resolution before escalation,” Fahmy stated.
Effective tools require clean, targeted data. “Since some critical devices don’t produce logs, packet data becomes vital for full visibility,” Wilk added.
Electric vehicle chargers, solar panels, and smart meters boost port efficiency and sustainability but also create new hacker entry points. “We’ve observed attacks on energy and connected devices in other sectors. Hackers aim to disrupt or gain long-term access. Without continuous packet-level monitoring, vulnerabilities may go unnoticed until too late,” Fahmy warned.
“Compromised vendor updates could install system backdoors. Continuous monitoring is crucial to identify all connected devices, automate password and software updates, and implement network separation to contain breaches,” Alzoubi advised.
To enhance port cybersecurity, Wilk suggests starting by identifying and addressing network coverage gaps, including OT, IoT, and cloud environments. Visibility blind spots often leave threats undetected, making comprehensive, end-to-end observability vital. Ensuring all cybersecurity tools receive high-quality, relevant network data is equally important.
Fahmy proposes a three-phase strategy — map and secure, fortify and automate, and test and train. “With comprehensive visibility and constant monitoring, ports replace uncertainty with uninterrupted operations,” he added.
“Establish dashboards to track key metrics like device uptime, problem detection speed, and issue resolution time. This provides port leadership visibility into cybersecurity performance without disrupting cargo operations,” Alzoubi concluded.